Banks scramble to comply with Central Bank's tight timeline for enhanced online protection regulations
Nigeria's financial institutions are scrambling to meet the Central Bank of Nigeria's June 10, 2026 deadline for implementing a new cyber-security baseline, a requirement that is proving to be a significant challenge for many operators. The deadline is fast approaching, and industry sources indicate that most commercial banks are on track to meet it, but smaller institutions are lagging behind.
nThe smaller institutions, which include microfinance banks and finance houses, are struggling to comply with the new baseline due to the absence of Chief Information Security Officers, or CISOs, a critical component in achieving the required cyber-security standards. This shortfall exposes the entire financial system to the very risks that the new baseline is intended to prevent.
nThe Central Bank of Nigeria introduced the new cyber-security standard to combat Anti-Money Laundering, Combating Financial Terrorism, and Counter-Proliferation Financing solutions, and issued a circular on March 10, 2026, directing all regulated financial institutions to submit an implementation roadmap by June 10, 2026. The circular, BSD/DIR/PUB/LAB/019/002, mandates a baseline standard for automated AML/CFT/CPF systems across all regulated financial institutions.
nAccording to Ms Seun Runsewe, a subject matter expert in cybersecurity, the circular covers 12 functional areas, each requiring a governance architecture, not just a system purchase, a daunting task for many smaller institutions. The leading banks, however, are likely to meet the deadline, given that they have CISOs, internal teams, and vendors already in place.
nRunsewe expressed concern that the majority of regulated institutions, including roughly 900 microfinance banks, over 100 finance houses, and primary mortgage banks, are not adequately prepared to meet the deadline, lacking even the basic infrastructure, such as a CISO or an automated AML solution. Many of these institutions are starting from scratch, with the deadline looming large.
nThe consequences of this gap are far-reaching, according to Runsewe, who noted that these under-instrumented institutions are part of a shared ecosystem, including NIBSS, BVN, and agency banking networks, which means that a breach in one institution can have ecosystem-wide implications. The larger banks, in particular, are vulnerable to inheriting the risks that arise from the weaknesses of smaller institutions.
Related Stories
 General News
CELEBRATING TWO YEARS OF TRANSFORMATIONAL LEADERSHIP IN THE PRESIDENTIAL AMNESTY PROGRAMME
Tomorrow, 14TH March 2026, as we look forward to the second anniversary, we reflect on the remarkable two years since the Administrator of the Preside
 General News
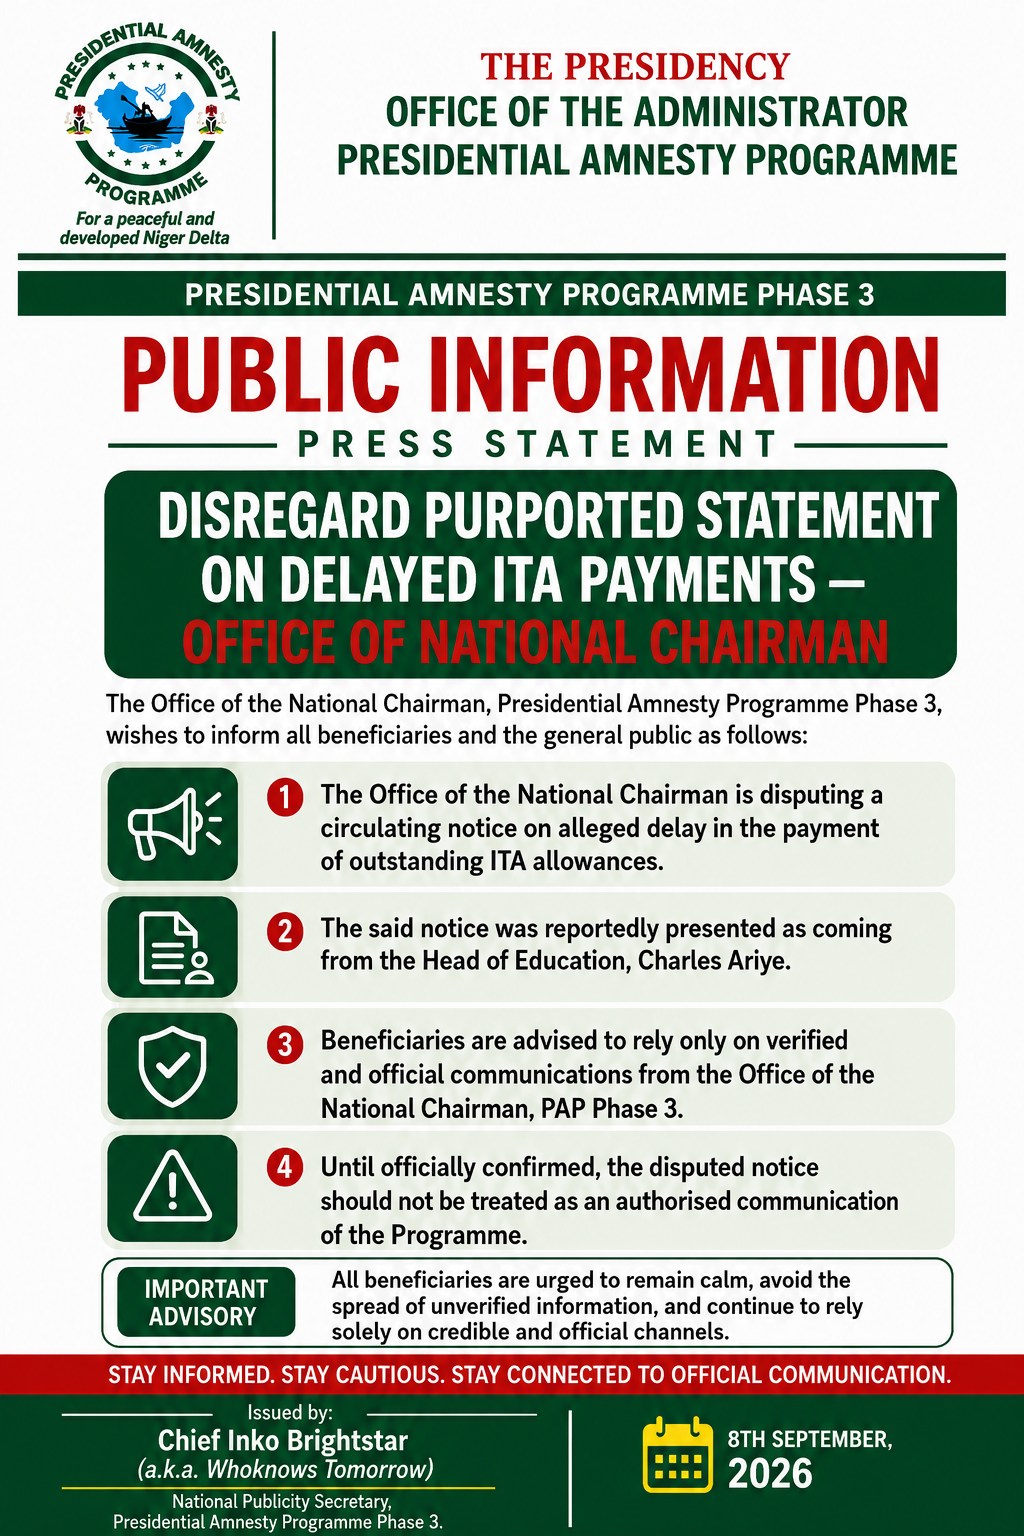
PRESIDENTIAL AMNESTY PROGRAMME PHASE 3: DISREGARD PURPORTED STATEMENT ON DELAYED ITA PAYMENTS — OFFICE OF NATIONAL CHAIRMAN
The Office of the National Chairman of the Presidential Amnesty Programme Phase 3, General Elaye ThankGod Dollar Slaboh, has called on beneficiaries a
 General News
RE: CLARIFICATION ON MY PERSONAL RELATIONSHIPS
PUBLIC NOTICErnrnRE: CLARIFICATION ON MY PERSONAL RELATIONSHIPSrnrnIt has become necessary to make this public clarification following the increasing